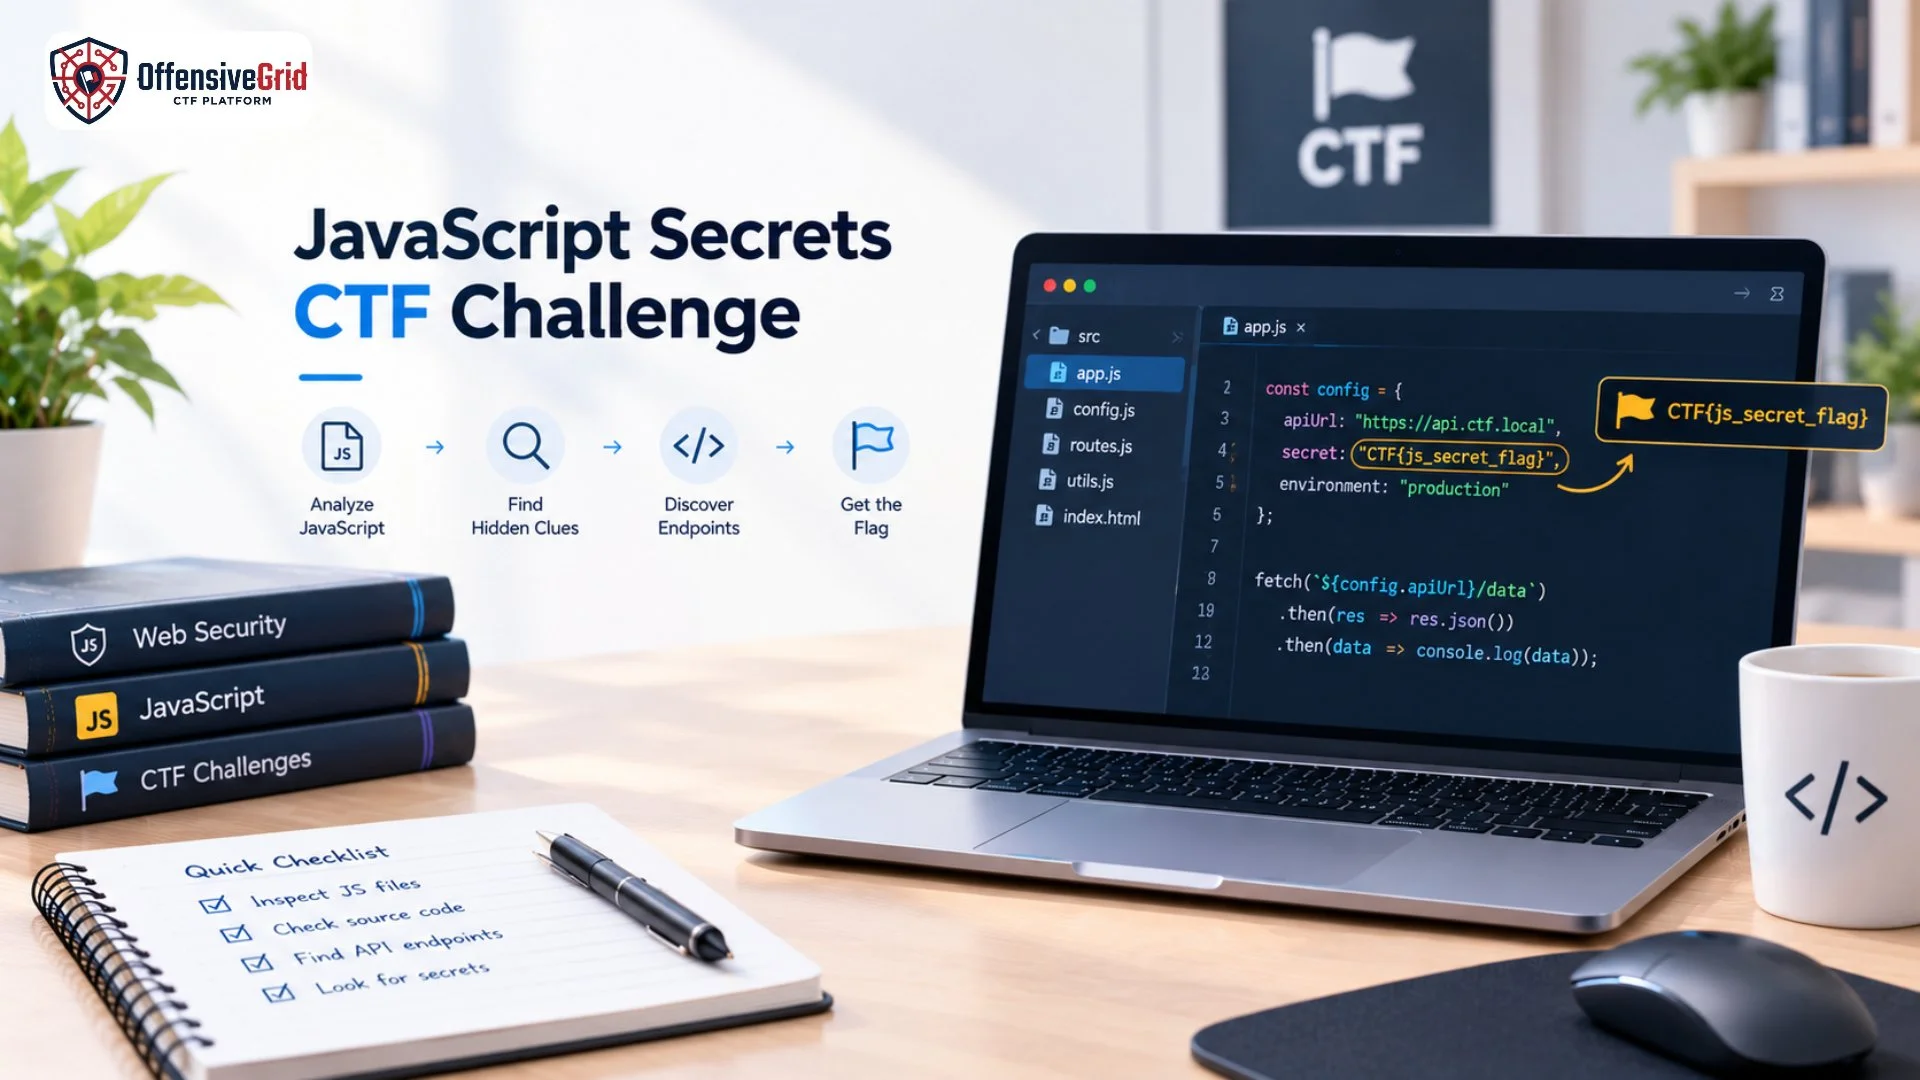
JavaScript Secrets CTF Challenge teaches you how sensitive information can be accidentally exposed through client-side JavaScript. CTFs may hide clues, API endpoints, configuration values, or secret strings inside JavaScript files.
This guide covers practical techniques for inspecting JavaScript, discovering hidden clues, and solving JavaScript secrets challenges in authorized CTF and lab environments.
What Is a JavaScript Secrets CTF Challenge?
A JavaScript Secrets CTF Challenge is a web-based challenge where participants investigate JavaScript code to find a hidden clue, endpoint, configuration value, or flag.
The challenge may contain information such as:
- API endpoints
- Test credentials
- Hidden routes
- Configuration values
- Challenge flags
- Feature flags
- Internal hostnames
- Developer comments
- Encoded values
- Source map references
For example, a deliberately vulnerable CTF application might contain:
const config = {
apiUrl: “/api/v1/users”,
environment: “test”,
challengeKey: “CTF{example_secret}”
};
The goal is not to attack a real application. Instead, the challenge teaches how information exposed to the browser can be inspected by a user.
Why Are JavaScript Files Important in CTFs?
Modern web applications frequently depend heavily on client-side JavaScript. Frontend applications can contain routes, API calls, feature information, and configuration data that is delivered to the browser. Because the browser must receive client-side code to execute it, users can inspect that code. OWASP notes that developers can accidentally expose sensitive information through frontend JavaScript, including API keys, internal IP addresses, sensitive routes, and credentials. This makes JavaScript analysis particularly useful in CTF challenges.
How to Solve a JavaScript Secrets CTF Challenge
1. Explore the CTF Application
Start by visiting the challenge normally. Do not immediately run automated tools. First, understand how the application works.
Check:
- Homepage
- Login page
- Registration page
- Dashboard
- Search functionality
- User profiles
- Forms
- API-based features
- Browser requests
- Error messages
Look for anything that indicates the application uses JavaScript.
You may see files such as:
/static/js/app.js
/assets/main.js
/js/script.js
/js/config.js
These files should become part of your investigation.
2. Inspect the HTML Source
Open the page source or browser developer tools.
Look for <script> elements such as:
<script src=”/js/app.js”></script>
<script src=”/static/js/config.js”></script>
These references tell you which JavaScript files are loaded by the page.
Also inspect HTML comments because developers may accidentally leave useful challenge clues in comments.
For example:
<!– TODO: remove test API endpoint –>
In a CTF, a clue like this may point toward another resource.
3. Review JavaScript Files
Open the JavaScript files directly and read through them.
Search for terms that may be relevant to the challenge, such as:
api
key
token
secret
password
admin
debug
test
internal
config
auth
endpoint
You may encounter variables such as:
const apiKey = “CTF_TEST_KEY”;
const adminRoute = “/hidden-admin”;
const debugMode = true;
In a real application, exposing sensitive credentials this way can be a security problem. In a CTF, however, such information may intentionally form part of the challenge.
4. Search for API Endpoints
JavaScript often contains API requests that are not obvious from the application’s interface.
Look for patterns such as:
fetch(“/api/users”);
fetch(“/api/admin”);
axios.get(“/api/config”);
These can reveal additional application functionality.
For example:
fetch(“/api/secret-data”)
may indicate that /api/secret-data is worth investigating within the CTF.
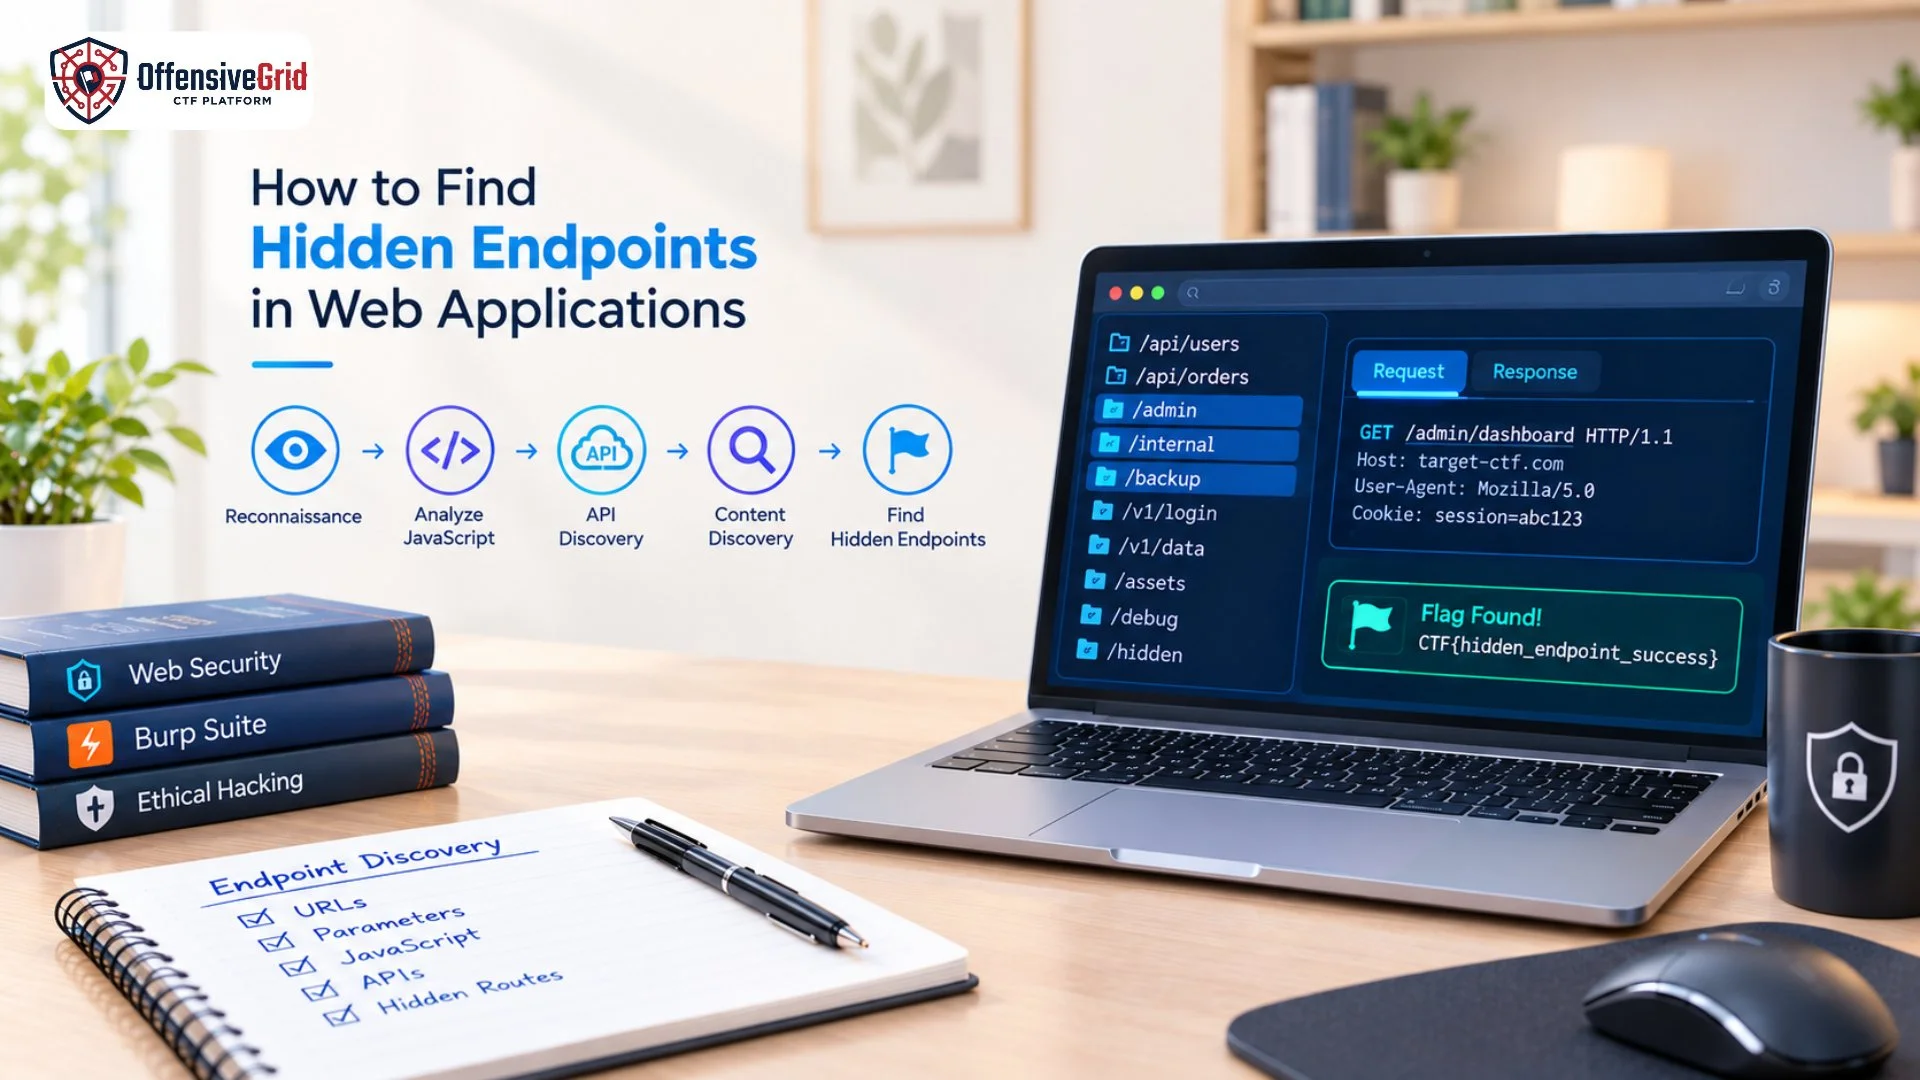
This technique also connects closely with how to find hidden endpoints in web applications, because JavaScript can reveal routes that are not directly linked through the visible interface.
5. Use Browser Developer Tools
Browser Developer Tools provide another useful way to investigate JavaScript. Open the Sources or Network panel and interact with the application.
Pay attention to:
- JavaScript files
- XHR requests
- Fetch requests
- API responses
- Request URLs
- Configuration objects
- Loaded resources
The Network panel can be particularly useful because some endpoints are generated only after a user acts.
For example, clicking a dashboard button might trigger:
GET /api/user/profile
while submitting a form might trigger:
POST /api/settings
These requests can reveal functionality that is not obvious from the page itself.
6. Search for Hardcoded Secrets
A common JavaScript secrets CTF technique is searching for values that look sensitive.
Possible patterns include:
const secret = “CTF{…}”;
const token = “test-token”;
const apiKey = “example-key”;
const username = “admin”;
You can also search for strings containing:
secret
token
key
password
credential
authorization
bearer
private
However, not every string resembling a secret is actually sensitive. Some applications contain placeholders, public identifiers, test values, or intentionally fake credentials. Your job is to understand the context.
7. Check JavaScript Source Maps
Some CTF challenges may expose source map files such as:
app.js.map
main.js.map
bundle.js.map
Source maps can connect minified JavaScript with its source code.
OWASP notes that publicly accessible source maps can expose information such as internal API paths, expected API fields, authorization logic, and hardcoded configuration values. If a challenge provides a source map, inspect it carefully because it may make the JavaScript significantly easier to understand.
8. Analyze Encoded Values
CTF authors sometimes encode clues rather than displaying them directly.
You might encounter:
Q1RGe2V4YW1wbGVfc2VjcmV0fQ==
The value may be Base64-encoded.
Other challenges might use:
- Hexadecimal
- URL encoding
- Simple substitutions
- Custom JavaScript functions
For example:
const value = atob(“Q1RGe2V4YW1wbGVfc2VjcmV0fQ==”);
indicates that the browser is decoding a Base64 value. Do not assume every encoded value is a secret. First determine how the application uses it.
Using Burp Suite for JavaScript CTF Challenges
Burp Suite can make JavaScript reconnaissance easier by allowing you to observe requests made by the application. If you are new to Burp, our guide on how to use Burp Suite explains interception, HTTP request analysis, Repeater, and other practical features.
With Burp Suite, you can examine:
- JavaScript requests
- API endpoints
- Parameters
- Responses
- Cookies
- Headers
- Redirects
- Loaded resources
You can also use its site mapping and content discovery capabilities to understand the application’s structure. The important principle is to combine automated discovery with manual analysis rather than relying entirely on one technique.
Common Clues in JavaScript Secrets CTFs
| Clue | What It May Reveal |
| apiKey | API-related value |
| token | Authentication or test token |
| /admin/ | Hidden route |
| debug=true | Development functionality |
| sourceMappingURL | Source map |
| fetch() | API request |
| axios.get() | API endpoint |
| password | Credential-related clue |
| config | Application configuration |
| HTML comments | Developer notes |
These examples are intended for controlled CTF challenges and security labs.
Practice JavaScript Secrets CTF Challenges on Offensive Grid
Finding secrets in JavaScript becomes much more useful when you can practice the complete workflow in a controlled environment.
Offensive Grid provides hands-on cybersecurity training with CTF ranges and practical labs, including web application security and penetration-testing scenarios. Its training platform is designed around isolated, real-world-style environments where learners can practice offensive and defensive techniques safely. Users can practice JavaScript reconnaissance, hidden endpoint discovery, API analysis, and related web security techniques through authorized CTF and lab environments on Offensive Grid.
This is especially useful because CTF practice lets you make mistakes, investigate clues, and repeat the workflow without testing against real systems.
Common Mistakes in JavaScript Secrets CTF Challenges
Only Looking at the Homepage
The flag may not be present in visible HTML. Always inspect loaded JavaScript and network requests.
Ignoring Minified JavaScript
Minified code can look confusing, but browser formatting tools can make it easier to inspect.
Searching Only for “Secret”
A challenge may hide its clue inside a configuration variable, API route, encoded string, or function rather than using an obvious secret variable.
Trusting Every API Key
A value that looks like an API key may be public, restricted, expired, or intentionally fake. Analyze its context rather than assuming it is exploitable.
Forgetting Authorization
Only investigate applications and CTF environments where you have explicit permission. Never use discovered credentials or secrets against systems outside the challenge scope.
A Simple JavaScript CTF Workflow
A structured workflow makes these challenges easier:
Open CTF Application
↓
Inspect HTML Source
↓
Identify JavaScript Files
↓
Review JavaScript
↓
Find Routes & API Calls
↓
Search for Interesting Values
↓
Check Source Maps
↓
Decode Relevant Clues
↓
Verify the Flag
The objective is to understand how the frontend works and follow the clues provided by the challenge.
Common JavaScript CTF Techniques to Practice
Once you understand the basic workflow, you can combine several techniques in a single challenge:
- Identify JavaScript files.
- Search for interesting variables and strings.
- Map API endpoints.
- Inspect Network requests.
- Check source maps.
- Follow hidden routes.
- Decode relevant values.
- Verify the discovered clue or flag.
This structured approach is more effective than randomly searching through large JavaScript bundles.
You can also combine these techniques with how to find hidden endpoints in web applications to build a broader understanding of web application reconnaissance.
FAQs
What is a JavaScript Secrets CTF Challenge?
It is a CTF challenge where participants inspect client-side JavaScript to discover hidden clues, routes, configuration values, encoded data, or flags.
Where should I look for secrets in JavaScript?
Start with JavaScript files loaded by the page, inline scripts, configuration objects, API requests, source maps, comments, and browser Network requests.
Can JavaScript reveal hidden API endpoints?
Yes. Client-side JavaScript can contain API request paths and application routes, making it useful during web application reconnaissance.
Are JavaScript secrets always vulnerabilities?
No. In a CTF, they may be intentionally exposed as part of the challenge. In real applications, however, sensitive credentials should not be placed in client-side code because browser-delivered code can be inspected by users.
Can Burp Suite help with JavaScript CTFs?
Yes. Burp Suite can help capture JavaScript requests, analyze API traffic, map application resources, and investigate endpoints.
Where can I practice JavaScript CTF challenges?
You can practice in authorized CTF platforms, deliberately vulnerable applications, private labs, and hands-on environments such as Offensive Grid, which provides CTF ranges and practical cybersecurity labs.
Conclusion
A JavaScript Secrets CTF Challenge is an excellent way to develop practical web reconnaissance and source-code analysis skills. Start by exploring the application, identifying JavaScript files, inspecting source code, analyzing API requests, searching configuration values, examining source maps, and carefully investigating encoded clues. The most important skill is not simply finding a suspicious string. It is understanding how the JavaScript connects different parts of the application and using those clues to solve the challenge systematically. For hands-on practice, users can apply these techniques in authorized CTF and lab environments such as Offensive Grid, where practical web security and CTF scenarios provide a controlled way to develop these skills.