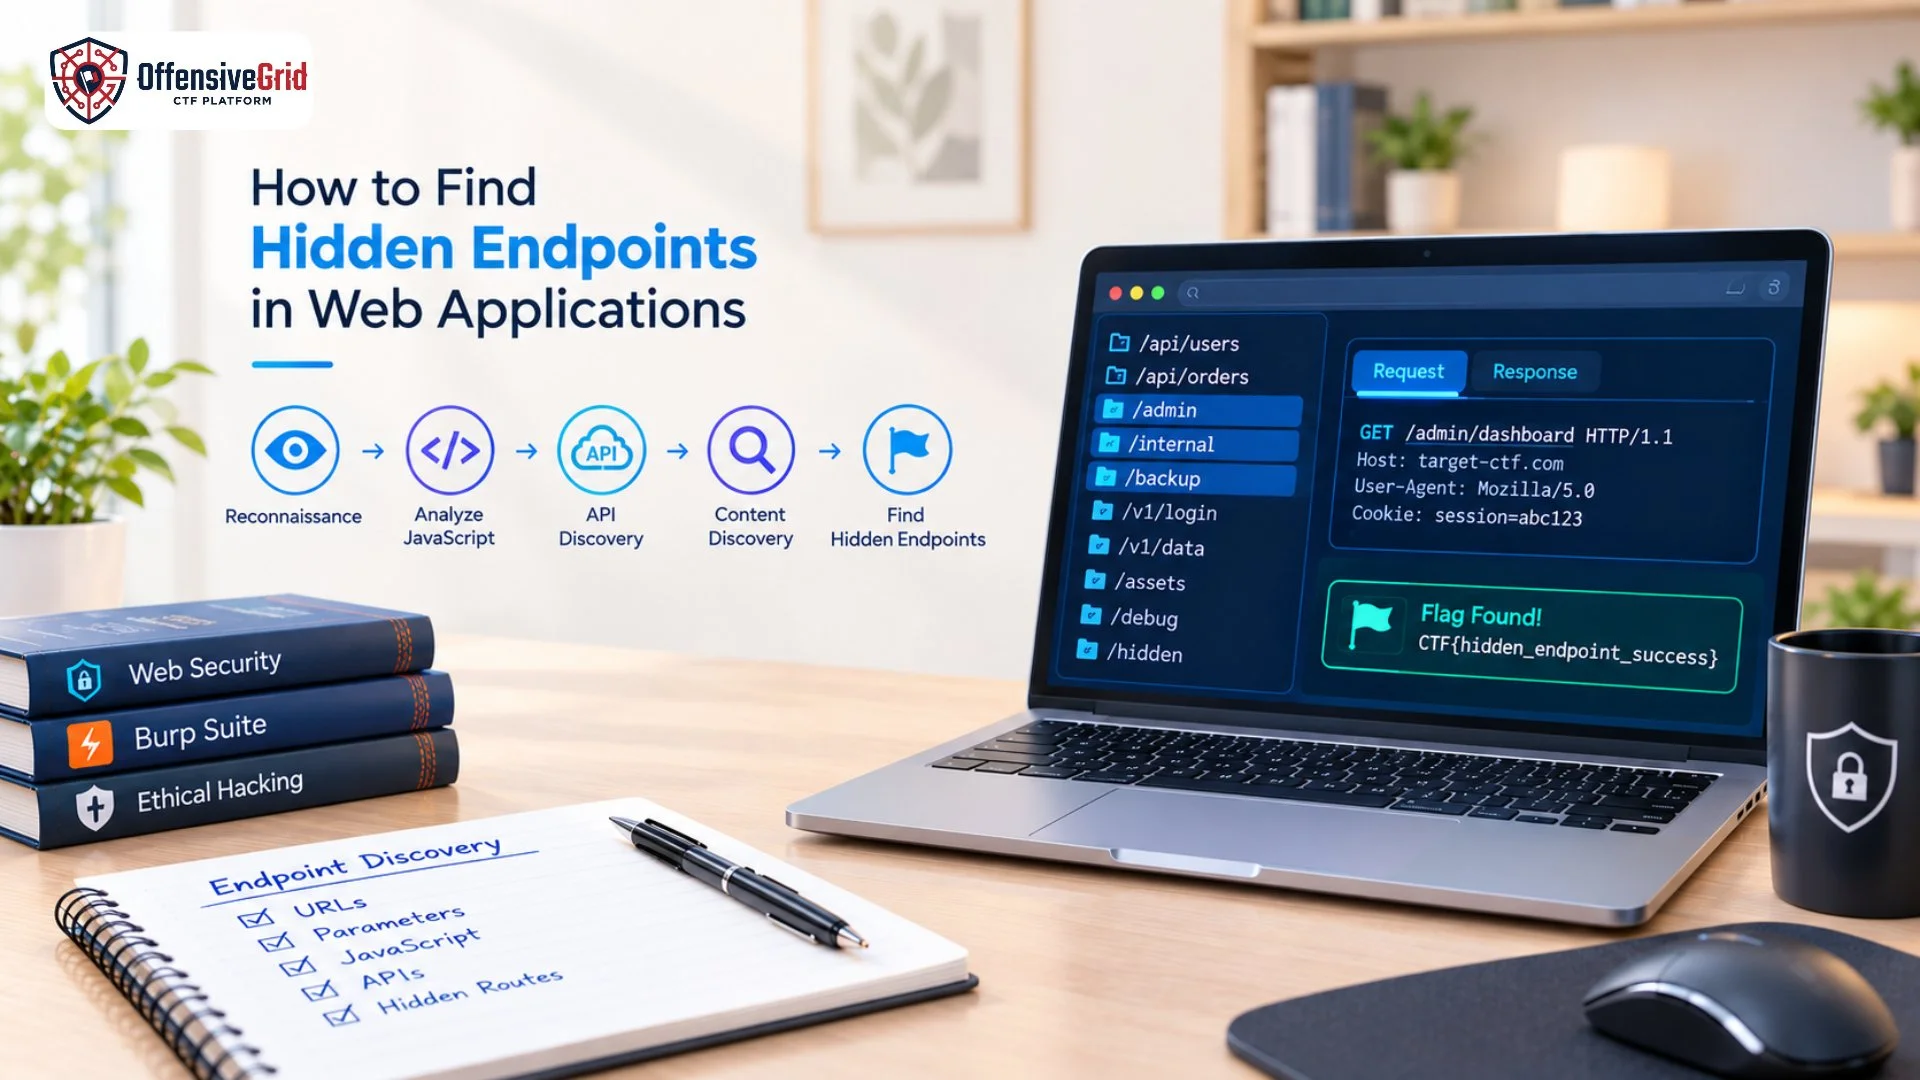
Modern web applications often contain APIs, admin panels, internal routes, and other resources that may not appear in the main navigation. Learning how to find hidden endpoints in web applications helps security professionals discover an application’s attack surface and identify functionality that needs further testing. In this guide, you’ll learn practical techniques using Burp Suite, JavaScript analysis, API reconnaissance, and content discovery in authorized labs and CTF environments.
What Are Hidden Endpoints in Web Applications?
A hidden endpoint is a URL, API route, function, or application resource that is not directly exposed through the application’s visible navigation.
For example, a website might visibly provide:
/dashboard
/profile
/products
/logout
But the application could also contain endpoints such as:
/api/users
/api/orders
/admin/users
/internal/reports
/backup
These endpoints may not appear as clickable links on the website.
Hidden endpoints are not automatically vulnerabilities. The security concern arises when undocumented or forgotten functionality is exposed without appropriate authentication, authorization, validation, or other security controls.
PortSwigger notes that hidden content can include testing functionality, newly added features, internal-only functionality, and features that a particular account does not have permission to use.
Why Finding Hidden Endpoints Matters
Endpoint discovery is an important part of web application reconnaissance because security testing depends on understanding the application’s attack surface.
An application may contain an endpoint that:
- Is not linked from the homepage
- Is only called by JavaScript
- Belongs to an API
- Is accessible only after authentication
- Uses undocumented parameters
- Belongs to an older application version
- Was left behind after development or testing
- Exists within a separate application path
OWASP describes application enumeration and attack-surface mapping as an important step before detailed security testing because it helps testers identify areas that require further investigation. Finding an endpoint does not mean exploiting it. The objective is first to understand what exists and then determine whether appropriate security controls are applied.
How to Find Hidden Endpoints in Web Applications
1. Explore the Application Manually
Start with normal browsing before using automated discovery tools. Visit every accessible feature and observe the requests generated by the application.
Pay attention to:
- Login and registration
- Search functionality
- Account settings
- User profiles
- File uploads
- Download functions
- Contact forms
- Admin functionality
- API requests
- Password reset workflows
Manual exploration provides important context for later endpoint discovery.
For example, if you discover:
/api/user/profile
you may notice that the application also uses related routes such as:
/api/user/settings
/api/user/orders
/api/user/preferences
These patterns can provide useful clues for further testing.
2. Inspect HTTP Requests With Burp Suite
An intercepting proxy is one of the most useful tools for understanding how a web application communicates with its backend.
Burp Suite can help you inspect:
- Request URLs
- HTTP methods
- Query parameters
- Request bodies
- Cookies
- Headers
- API requests
- Server responses
OWASP recommends paying attention to both GET and POST requests, their parameters, hidden form fields, cookies, and other request components when identifying application entry points. For a detailed introduction to the tool, see how to use Burp Suite.
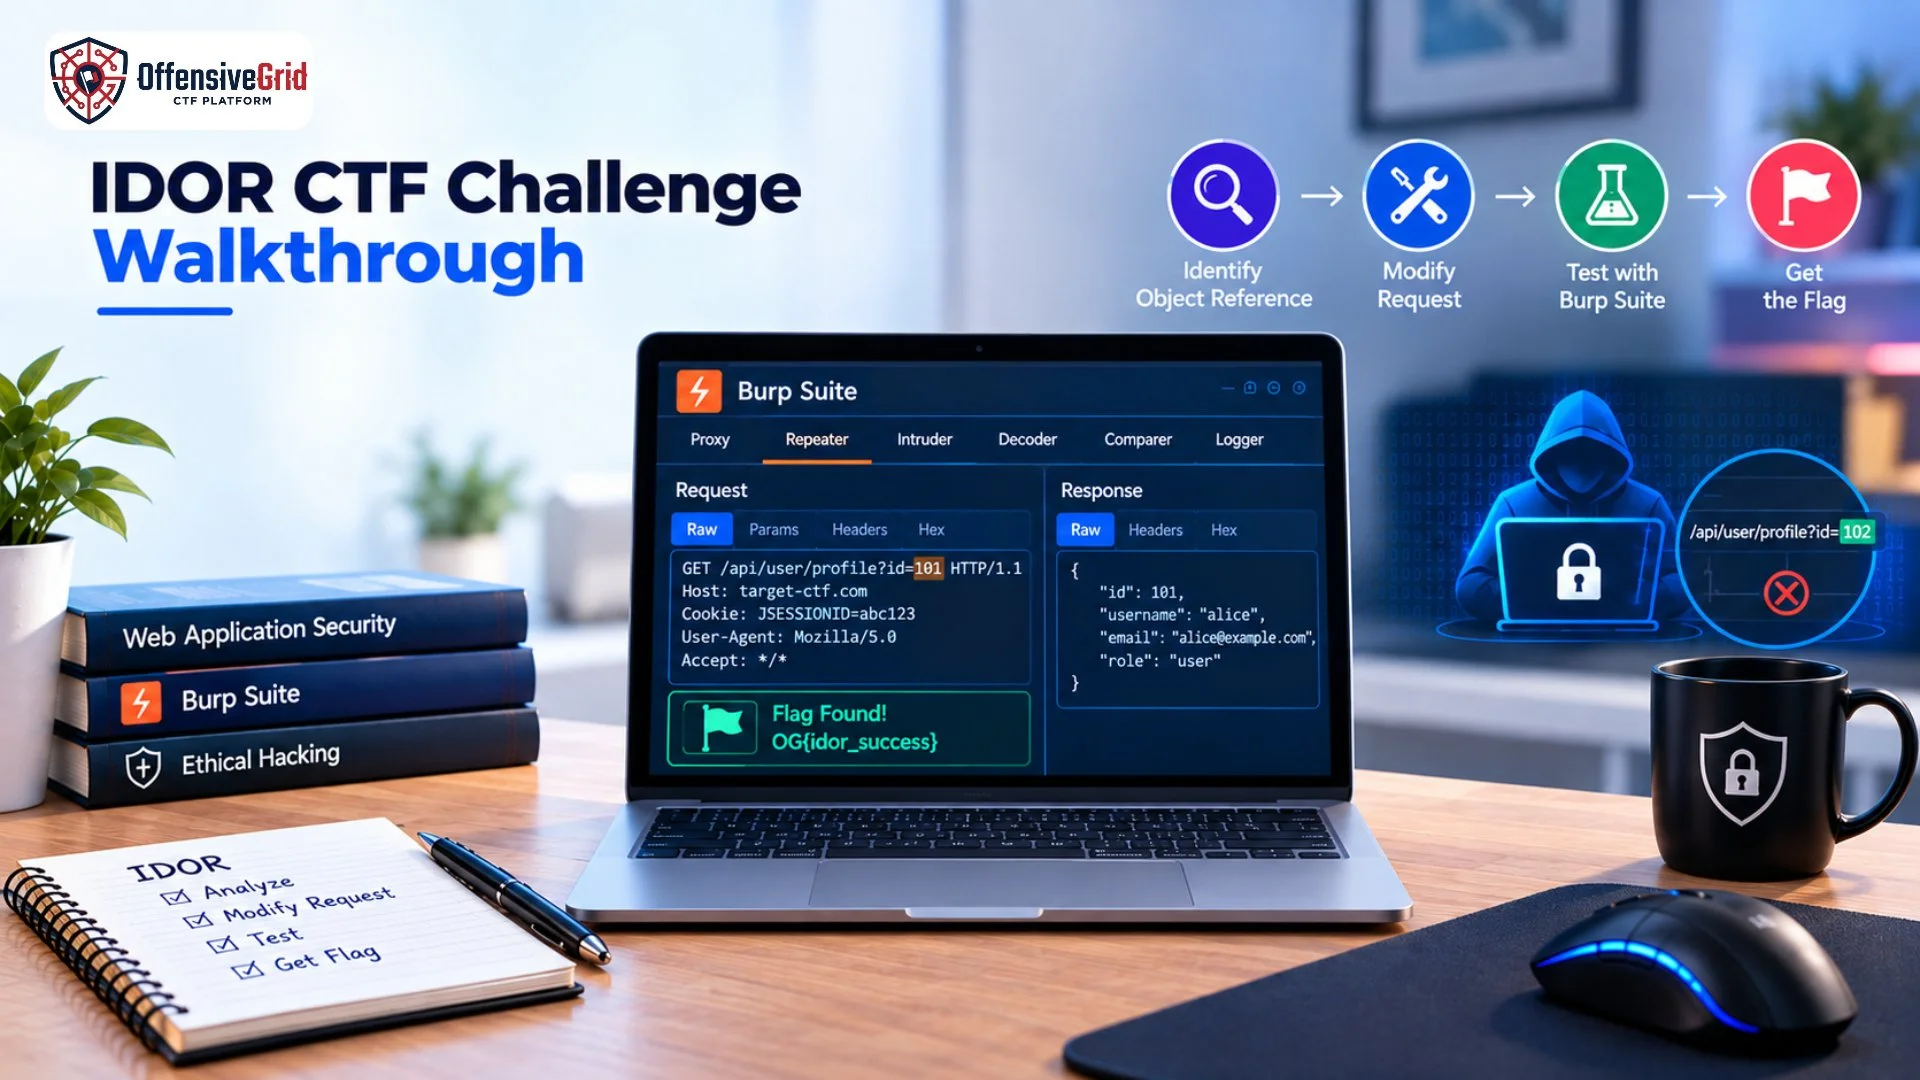
For example, a request might look like:
GET /api/user/profile?id=101 HTTP/1.1
Host: ctf.example
Cookie: session=abc123
The request itself may reveal an API structure or object reference that was not visible through the application’s interface.
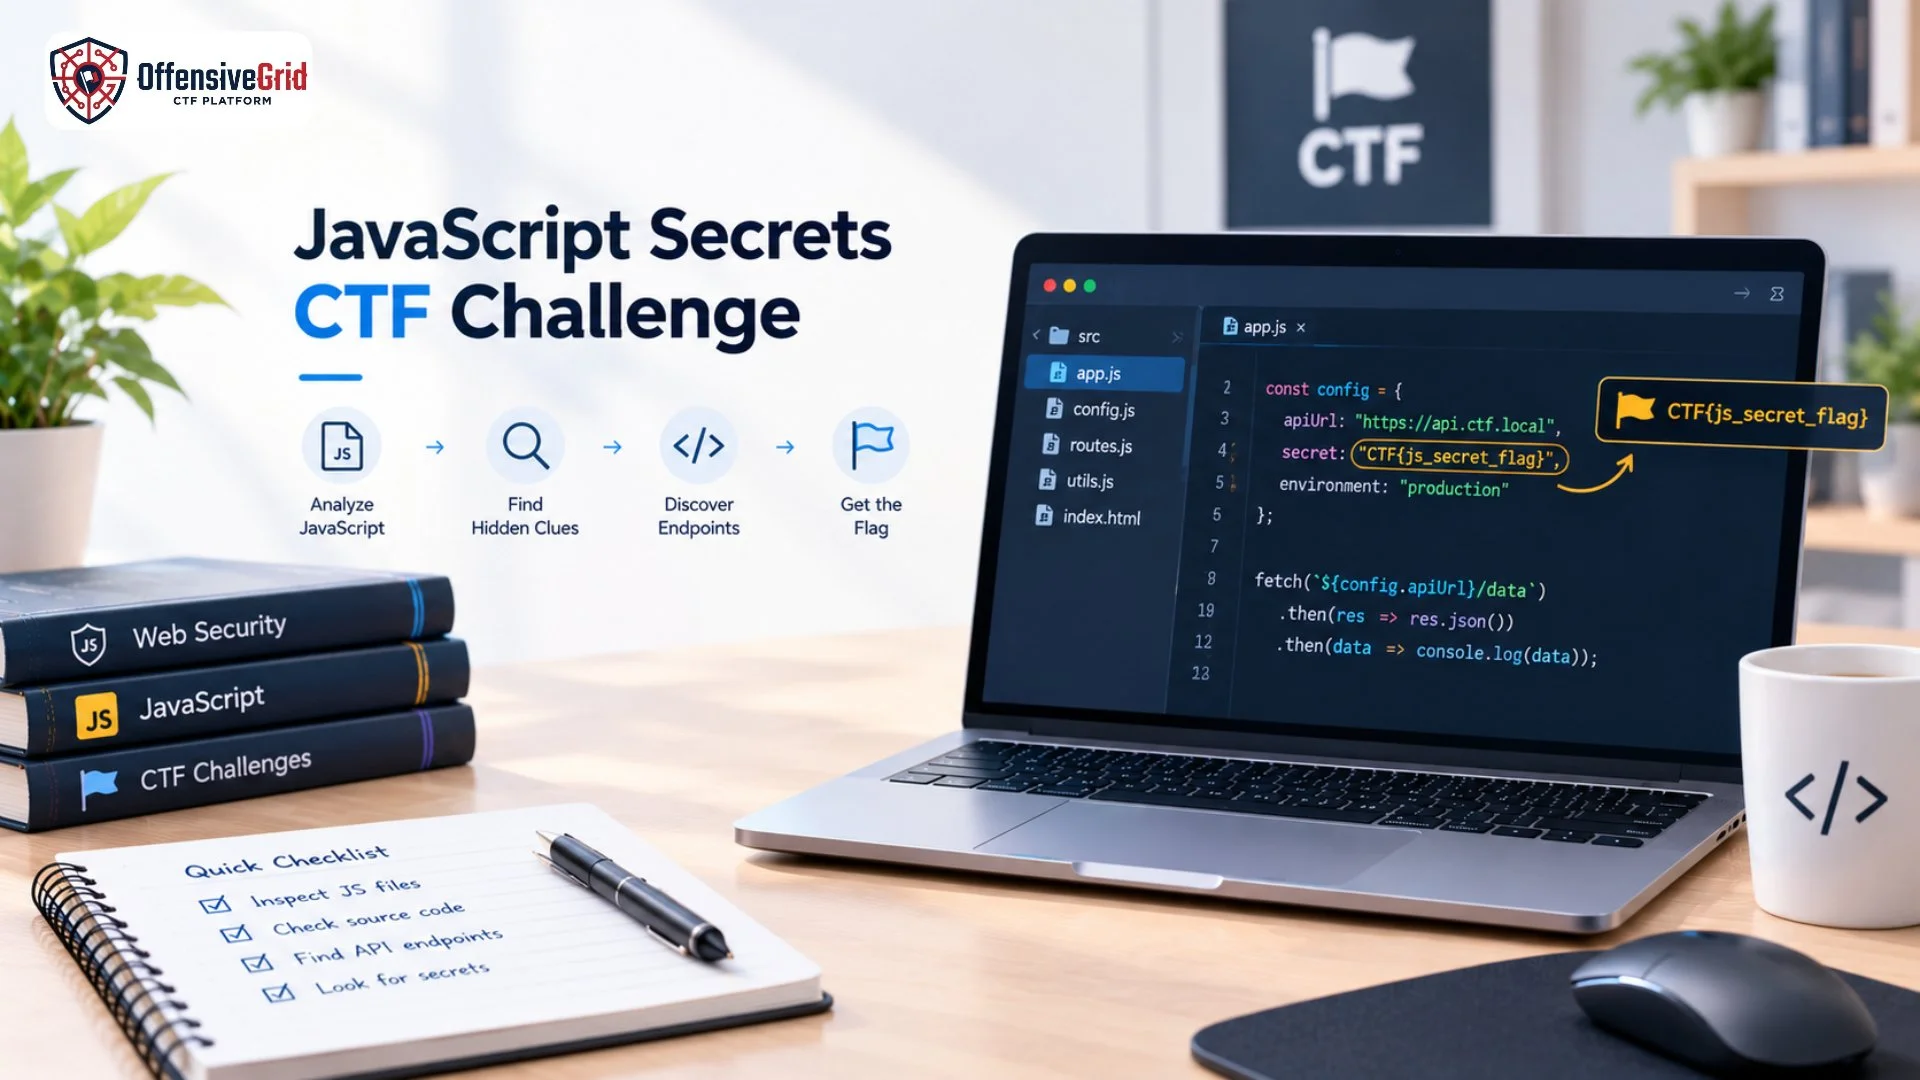
3. Analyze JavaScript Files
Modern web applications often use JavaScript to communicate with backend APIs and dynamically load content.
JavaScript files may contain references to:
/api/
/admin/
/internal/
/v1/
/v2/
/users/
/download/
You can search JavaScript for patterns such as:
fetch(
axios. get(
axios. post(
XMLHttpRequest
/api/
OWASP’s current testing guidance notes that client-side source analysis can reveal API endpoints, feature information, and other application details. This technique can be particularly useful for single-page applications where many routes are loaded dynamically rather than appearing as traditional HTML links.
4. Check robots.txt and Sitemap Files
Files such as:
/robots.txt
/sitemap.xml
can sometimes reveal useful information about an application’s structure.
A robots.txt file may contain paths that website administrators do not want search engines to crawl. These paths are not automatically protected, so their presence should not be interpreted as a security control. Similarly, sitemap files can expose pages that are not obvious from normal navigation. Treat these files as reconnaissance sources rather than proof that a particular endpoint is vulnerable.
5. Look for Naming Patterns
Once you identify several endpoints, analyze their naming conventions.
For example:
/api/v1/users
/api/v1/products
/api/v1/orders
may suggest that the application follows a predictable API structure.
Another example could be:
/account/view
/account/edit
/account/settings
These patterns can help you understand how the application organizes its functionality. However, guessed endpoints should always be verified. A predictable naming pattern does not mean that every related endpoint actually exists.
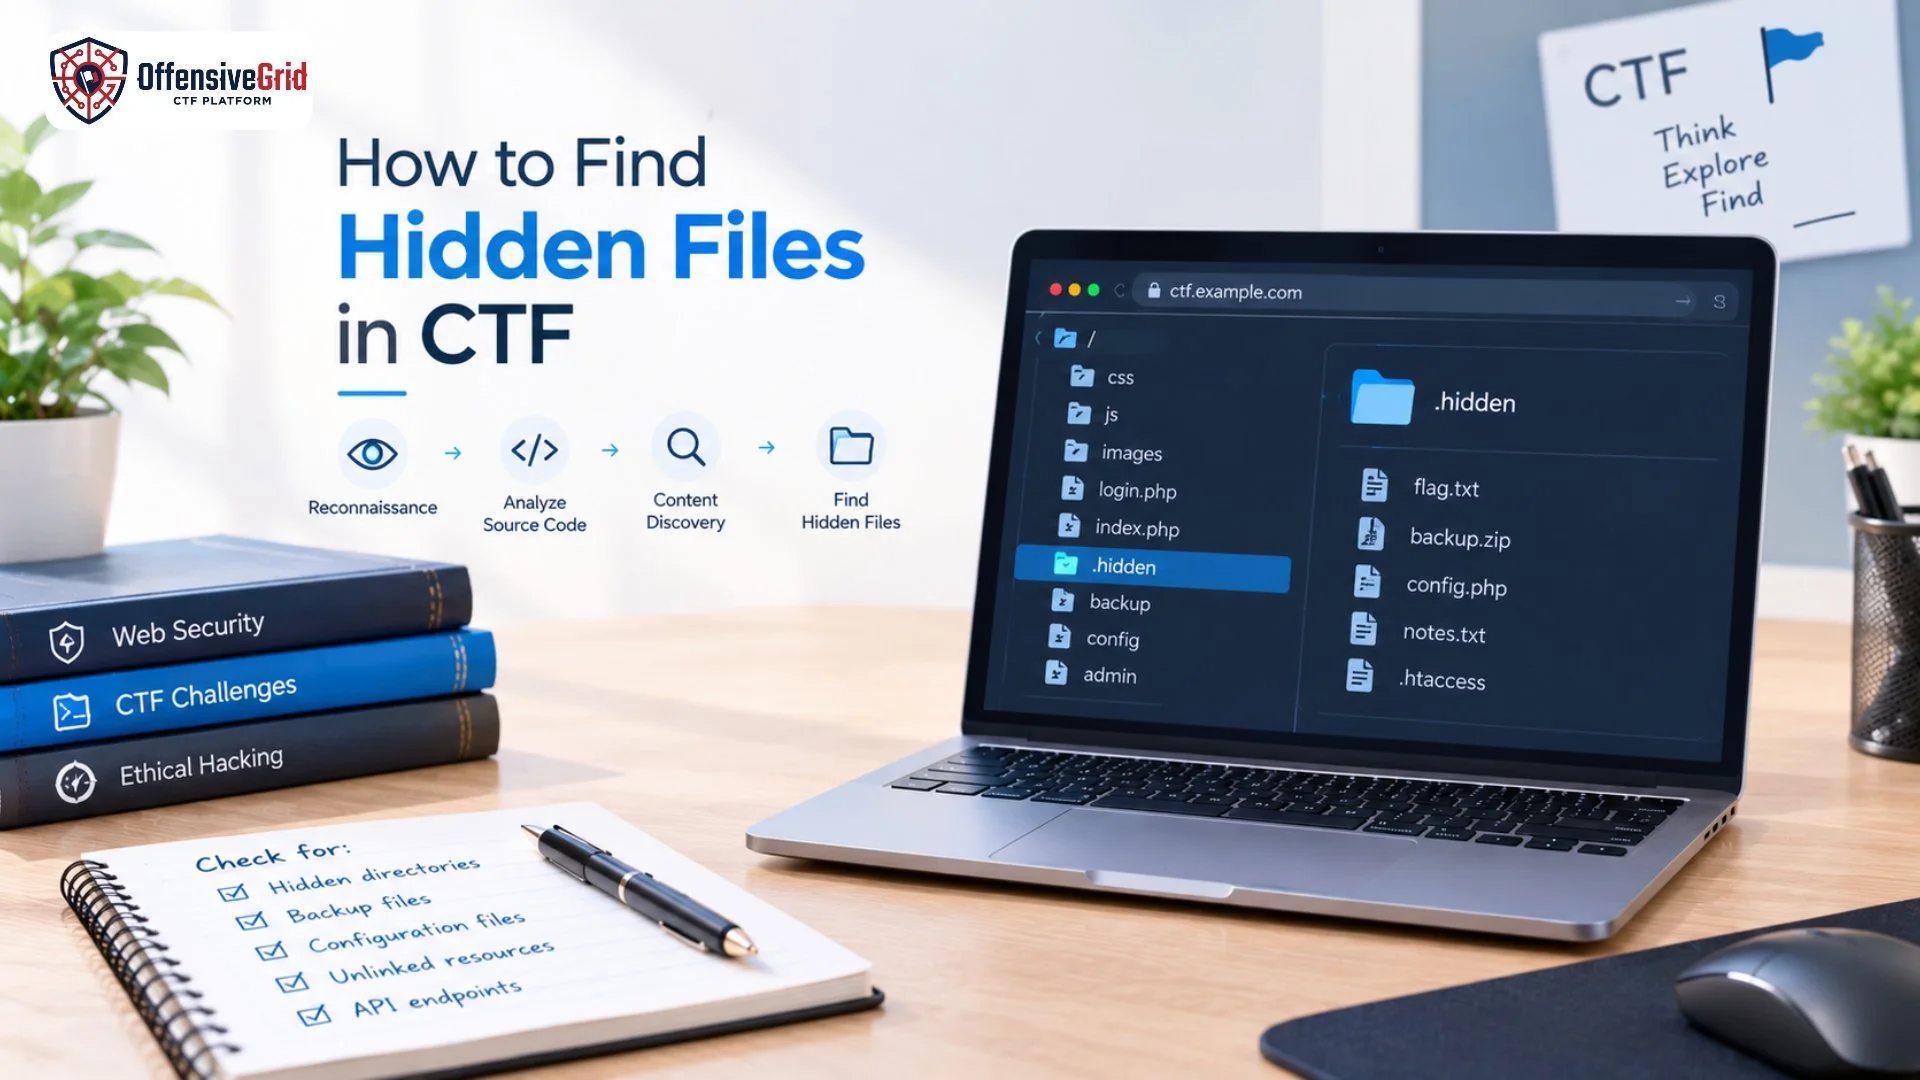
6. Use Content Discovery Tools
Automated content discovery can help identify directories, files, and functionality that are not linked from visible content. Burp Suite’s Content Discovery feature can use name guessing, crawling, and naming conventions to discover additional content and expand the application’s site map.
Other commonly used tools in authorized security labs include:
- ffuf
- Feroxbuster
- Gobuster
- OWASP ZAP
- Burp Suite
For example, a controlled lab might be tested against a wordlist containing paths such as:
admin
api
backup
dashboard
uploads
internal
test
The important step is to manually verify the results. A response from a guessed path does not automatically mean that useful functionality exists there.
7. Investigate API Endpoints
APIs are especially important when learning how to find hidden endpoints in web applications. A visible webpage may communicate with several backend endpoints that users never see directly.
For example:
GET /api/products
GET /api/products/25
POST /api/orders
PUT /api/profile
Inspect requests generated by the frontend and look for API documentation, OpenAPI specifications, Swagger interfaces, and versioned API paths.
OWASP recommends analyzing complete API requests, including URL parameters, request bodies, headers, and URL patterns, because important parameters may not be obvious from the visible application.
8. Check Different HTTP Methods
An endpoint can behave differently depending on the HTTP method being used.
For example:
GET /api/account
POST /api/account
PUT /api/account
DELETE /api/account
The existence of one method does not automatically mean that all other methods are supported. In an authorized testing environment, examining supported methods can help identify additional application functionality. However, avoid modifying important resources unnecessarily. Use test accounts and low-impact objects whenever possible.
How to Analyze Discovered Endpoints
Finding an endpoint is only the beginning. Each discovered endpoint should be documented and assessed.
A simple endpoint inventory can look like this:
| Endpoint | Method | Authentication | Purpose | Testing Focus |
|---|
/api/users |
GET | Required | User data | Authorization |
/api/orders |
GET | Required | Orders | Object access |
/admin |
GET | Required | Admin panel | Role restrictions |
/backup |
GET | None | File/resource | Exposure |
Then examine whether the endpoint properly handles:
- Authentication
- Authorization
- Input validation
- Sensitive information
- HTTP methods
- Error handling
- Rate limiting
- User and role separation
An endpoint being difficult to discover does not provide effective security by itself. Sensitive functionality should still enforce proper access controls.
Hidden Endpoints and Modern Web Applications
Modern applications can be difficult to map because functionality may be loaded dynamically through JavaScript, APIs, client-side routing, or multi-step workflows. OWASP notes that basic spidering can miss routes that are only reached through client-side navigation or API calls. Manual interaction through an intercepting proxy can therefore remain important for reaching authenticated or conditional functionality. This is why effective endpoint discovery usually combines several techniques rather than relying on one automated scanner.
A practical workflow is:
Manual Exploration
↓
Capture HTTP Requests
↓
Analyze JavaScript & APIs
↓
Identify Naming Patterns
↓
Run Content Discovery
↓
Verify Endpoints
↓
Map Attack Surface
↓
Begin Security Testing
Common Mistakes During Endpoint Discovery
Relying Only on Automated Tools
Automated discovery tools are useful, but they can miss application-specific functionality. Manual exploration, JavaScript analysis, and API inspection can reveal additional routes.
Treating Every Response as a Finding
A 200 OK response does not automatically indicate a security issue. Always examine the response content and understand what the endpoint actually does.
Ignoring APIs
Modern web applications can rely heavily on APIs. Focusing only on visible webpages may leave a significant part of the application’s attack surface unexplored.
Forgetting Authentication Context
An endpoint may return different information depending on the user’s session or role. Test relevant access levels only when authorized.
Testing Outside the Scope
Endpoint discovery can generate many requests. Always stay within the defined scope of the security assessment, CTF, or training environment.
Practice Hidden Endpoint Discovery Safely
The safest way to develop endpoint discovery skills is through CTFs, deliberately vulnerable applications, private labs, and authorized penetration testing environments. You can combine endpoint discovery with the broader methodology covered in Penetration Testing Steps and Phases to understand how reconnaissance and attack-surface mapping fit into a complete security assessment. Offensive Grid can also provide a controlled environment for hands-on cybersecurity training, CTF-style exercises, reconnaissance practice, and web security testing. Practicing in controlled environments helps you develop the skills needed to discover endpoints without accidentally interacting with systems you do not have permission to test.
FAQs
What are hidden endpoints in web applications?
Hidden endpoints are URLs, API routes, or application functions that are not directly visible through normal website navigation.
What is the easiest way to find hidden endpoints?
Start by manually exploring the application and inspecting HTTP traffic with Burp Suite. Then analyze JavaScript, API requests, naming patterns, and authorized content-discovery results.
Can JavaScript reveal hidden endpoints?
Yes. Client-side JavaScript can contain API routes, internal paths, feature information, and other references that are not visible through the application’s interface.
Are hidden endpoints automatically vulnerabilities?
No. An endpoint being undocumented or difficult to find is not itself a vulnerability. Security issues arise when exposed functionality lacks appropriate security controls.
Which tools can help find hidden endpoints?
Burp Suite, OWASP ZAP, ffuf, Feroxbuster, and Gobuster can assist with endpoint and content discovery in authorized security testing environments.
Conclusion
Understanding how to find hidden endpoints in web applications is an important web security skill. Effective endpoint discovery combines manual exploration, HTTP traffic analysis, JavaScript inspection, API reconnaissance, naming-pattern analysis, and controlled content discovery. The goal is not simply to find as many URLs as possible. A strong security assessment builds an accurate map of the application’s attack surface and then evaluates whether discovered endpoints have appropriate authentication, authorization, input validation, and security controls. With regular practice in CTFs and authorized security labs, endpoint discovery can become a valuable part of a structured web application penetration testing methodology.